Legal Cyber Academy

Decrypting the Threat: How to Protect Your Organization from Ransomware Risk

Taught by Daniel B. Garrie

RansomwareLevel: Intermediate1h 3m

Free preview of this course

A 5-minute excerpt from this course. The full course continues from where this leaves off.

Overview of Decrypting the Threat: How to Protect Your Organization from Ransomware Risk

Technical and legal experts provide an overview of ransomware and the current threat landscape, then cover key technical risk management practices alongside non-technical considerations such as tabletop exercises, the OFAC Ransomware Advisory, and disclosures under the 2023 SEC cybersecurity rules. The session concludes with strategies to mitigate ransomware risk across business functions.

What you’ll learn in Decrypting the Threat: How to Protect Your Organization from Ransomware Risk

  • Understand ransomware and the risks it entails
  • Apply key technical risk management practices
  • Address non-technical considerations including OFAC advisories and SEC disclosures
  • Coordinate ransomware risk mitigation across business functions

Audience and prerequisites

Who should take this courseDecrypting the Threat: How to Protect Your Organization from Ransomware Risk

Attorneys, IT, HR, and compliance professionals coordinating ransomware risk management.

Curriculum

  1. 1. Decrypting the Threat: How to Protect Your Organization From Ransomware Risk

    What You Will Learn In this seminar, our technical and legal experts begin by providing an overview of ransomware, the current threat landscape, and what information is being targeted by malicious actors. Next, our panelists touch on some of the key technical risk management practices organizations should adopt, before diving into the non-technical considerations against ransomware risk. These include conducting tabletops, knowledge of the OFAC Ransomware Advisory, and making the necessary disclosures according to the new 2023 SEC Cybersecurity Rules. Our speakers conclude this dynamic discussion with some of the key strategies for mitigating ransomware risks across business functions. Topics covered in this seminar include: Understanding Ransomware and the Risks it Entails Review of

    Locked

Your instructors

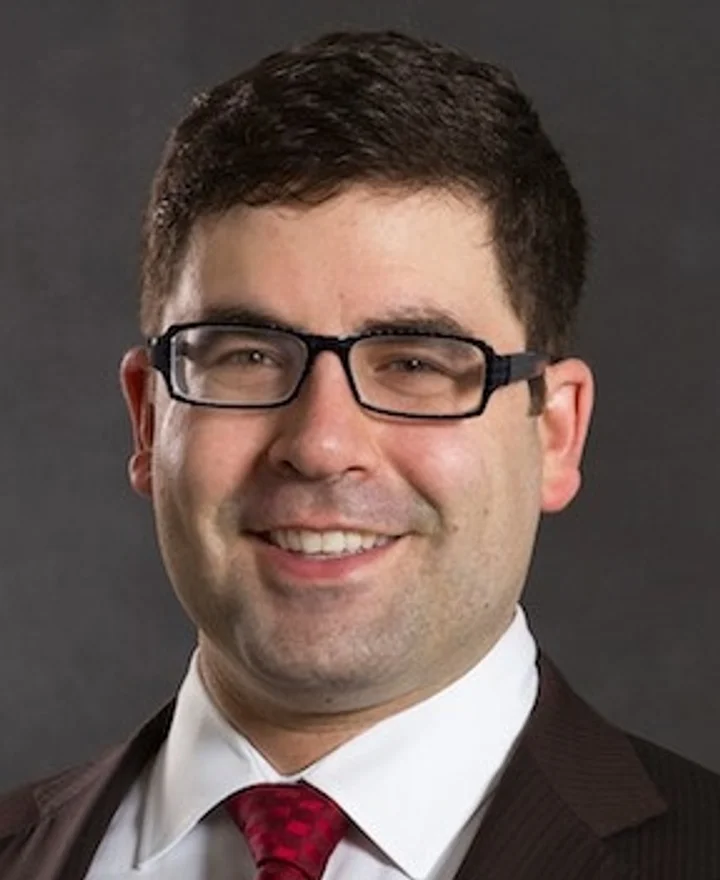
Portrait of Daniel B. Garrie

Daniel B. Garrie

Founder, Law & Forensics; Neutral at JAMS; Faculty at Harvard

Law & Forensics LLC · JAMS · Harvard · Rutgers Law School · Journal of Law & Cyber Warfare

Daniel B. Garrie is the founder and executive managing partner of Law & Forensics LLC, a boutique cybersecurity and forensic engineering firm he co-founded in 2008. He serves as a neutral, arbitrator, and forensic special master at JAMS, focusing on cybersecurity, cryptocurrency, and complex technology disputes, and holds faculty appointments at Harvard and Rutgers Law School. A patented software inventor and prolific author, he is editor-in-chief of the Journal of Law & Cyber Warfare and a widely cited authority on computer forensics, eDiscovery, and cyber litigation.

Portrait of Menachem Shafran

Menachem Shafran

SVP, Strategy and Innovation, XM Cyber

Menachem Shafran is Senior Vice President for Strategy and Innovation at XM Cyber, with more than 15 years of experience in product management and cybersecurity. He previously served five years in the Israel Defense Forces' Unit 8200, the military's elite intelligence unit, working as a researcher and team leader. His work centers on attack path management — how attackers actually move laterally through a network to reach critical assets — and he writes and speaks regularly on ransomware and cloud attack techniques. At Legal Cyber Academy he teaches on protecting an organization from ransomware risk.

Portrait of Tamara Snowdon

Tamara Snowdon

Head of Cyber Risk Wordings, Beazley

Tamara Snowdon is a cyber insurance specialist and head of cyber risk wordings at Beazley. She was previously a Senior Vice President in Marsh's Cyber, Media and E&O practice and its Cyber Coverage Leader, where she developed tailored coverage solutions, managed insurer product relationships, and built alternative risk transfer programs including captives. Before joining Marsh she worked in the cyber and technology E&O national practice at Beecher Carlson, at the Federal Trade Commission, and in the Economic Crimes Bureau of the Queens County District Attorney's Office. At Legal Cyber Academy she teaches on protecting an organization from ransomware risk.

Portrait of Cory Simpson

Cory Simpson

Founder and CEO, Gray Space Strategies, Inc.

Gray Space Strategies

Cory Simpson is the founder and CEO of Gray Space Strategies, Inc., a professional services and strategic advisory firm based in Washington, D.C. He has over twenty years of experience across government, the military and the private sector, assisting clients in navigating the U.S. government, emerging technology markets, the cybersecurity ecosystem and national security. Before founding Gray Space Strategies he was a managing director at Ankura and an executive vice president at Resolute Strategic Services. He served on active duty in the Army Judge Advocate General's Corps from 2004 to 2016, spending most of that career as a general counsel in the special operations and airborne communities, a prosecutor and a national security law advisor, and he continues to serve in the Army Reserve as a legal advisor to the U.S. Army Cyber Command. He is a senior advisor to the Cyberspace Solarium Commission (CSC 2.0) and an adjunct senior fellow with the Technology and National Security Program at the Center for a New American Security. At Legal Cyber Academy, Cory Simpson teaches on cybersecurity executive orders and ransomware risk.

$19.99

No account needed — we’ll set one up with your email after checkout.