Legal Cyber Academy

Cybersecurity Issues in Healthcare: Threats and Regulations (Part 2 of 2)

Taught by Daniel B. Garrie

Privacy LawLevel: Intermediate1h 10m

Free preview of this course

A 5-minute excerpt from this course. The full course continues from where this leaves off.

Overview of Cybersecurity Issues in Healthcare: Threats and Regulations (Part 2 of 2)

Part 2 of a two-part webinar on cybersecurity in healthcare, the most-targeted industry for data breaches. This session reviews the five titles of HIPAA, provides an overview of the HIPAA Privacy and Security Rule, and discusses proposed amendments, the enforcement rule, and violations. It concludes by breaking down the HITRUST Common Security Framework (CSF).

What you’ll learn in Cybersecurity Issues in Healthcare: Threats and Regulations (Part 2 of 2)

  • Identify the five titles of HIPAA and their scope
  • Apply the HIPAA Privacy and Security Rule
  • Understand HIPAA enforcement, violations, and proposed amendments
  • Describe the HITRUST Common Security Framework (CSF)

Audience and prerequisites

Who should take this courseCybersecurity Issues in Healthcare: Threats and Regulations (Part 2 of 2)

Attorneys advising healthcare businesses on cybersecurity risk and compliance.

Prerequisites for Cybersecurity Issues in Healthcare: Threats and Regulations (Part 2 of 2)

Part 1 of this two-part series recommended.

Curriculum

  1. 1. Cybersecurity Issues in Healthcare: Threats and Regulations Part 1 of 2

    In part one (1) of this seminar, our expert panelists discuss the current state of cybersecurity and healthcare, highlighting the most significant threats faced by the industry. Our speakers then focus on the Health Insurance Portability and Accountability Act (HIPAA) of 1996, reviewing its coverage and uses from their perspectives as attorneys or CISOs in healthcare. Topics covered in this webinar: The Current State of Cybersecurity Law and Healthcare Introduction to the Health Insurance Portability and Accountability Act of 1996 (HIPAA)

    Locked
  2. 2. Cybersecurity Issues in Healthcare: Threats and Regulations Part 2 of 2

    In part two (2) of this seminar, our expert panelists begin by reviewing the five titles of HIPAA. Our speakers then give an overview of the HIPAA Privacy and Security Rule and discuss Proposed HIPAA Amendments, its enforcement rule, and HIPAA violations. Finally, they conclude by breaking down the essential elements of the Health Information Trust Alliance Common Security Framework (HITRUST CSF). Topics covered in this webinar: The Five Titles of HIPAA HIPAA Privacy and Security Rule HIPAA Enforcement Rule, Violations, and Proposed Amendments Health Information Trust Alliance Common Security Framework (HITRUST CSF)

    Video coming soon

Your instructor

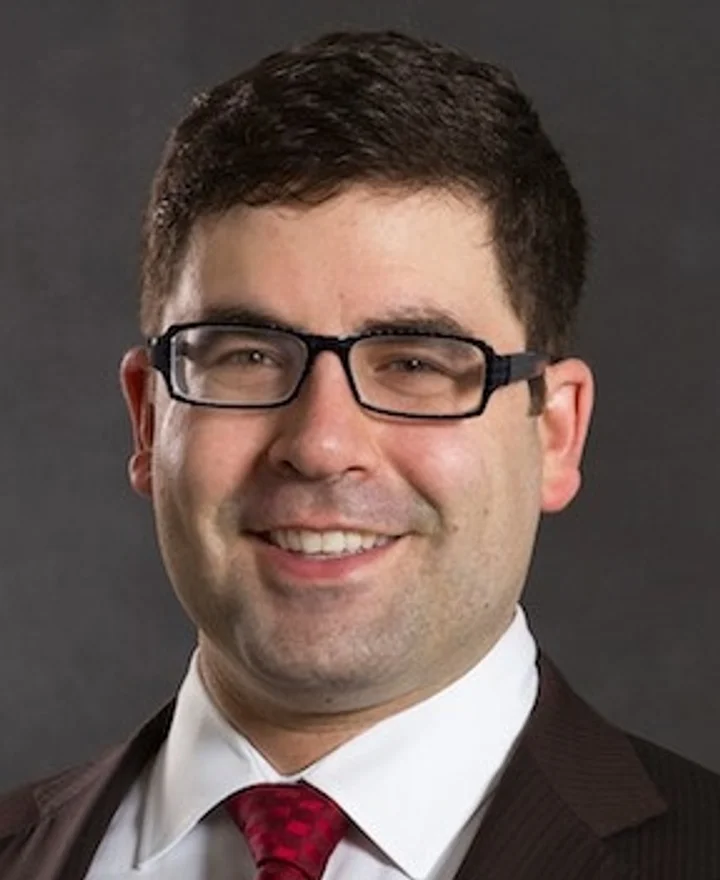
Portrait of Daniel B. Garrie

Daniel B. Garrie

Founder, Law & Forensics; Neutral at JAMS; Faculty at Harvard

Law & Forensics LLC · JAMS · Harvard · Rutgers Law School · Journal of Law & Cyber Warfare

Daniel B. Garrie is the founder and executive managing partner of Law & Forensics LLC, a boutique cybersecurity and forensic engineering firm he co-founded in 2008. He serves as a neutral, arbitrator, and forensic special master at JAMS, focusing on cybersecurity, cryptocurrency, and complex technology disputes, and holds faculty appointments at Harvard and Rutgers Law School. A patented software inventor and prolific author, he is editor-in-chief of the Journal of Law & Cyber Warfare and a widely cited authority on computer forensics, eDiscovery, and cyber litigation.
Learning track

Part of a learning trackPrivacy & Data Protection LawCourse 7 of 8 — see the full path
$39.99

No account needed — we’ll set one up with your email after checkout.